
Multi-Tenant
A group of companies often has one Microsoft Entra tenant per company: the parent company, its subsidiaries, a branch abroad. Multi-Tenant collects the devices of all these tenants in a single Device Inventory Manager, so that warranties, rentals, assets and reports cover the whole group.
The other tenants are registered as sub-tenants of yours:
- their devices are synchronized from their Microsoft Intune into your portal;
- they have no users, license or portal of their own: everything is managed from your tenant;
- every device keeps the company it belongs to, so you can filter by company and limit visibility by company.
A tenant that is already a Device Inventory Manager customer with its own license cannot be added as a sub-tenant.
Registering a sub-tenant
Open My Tenant › Edit › Information and scroll to the Multi Tenant card.
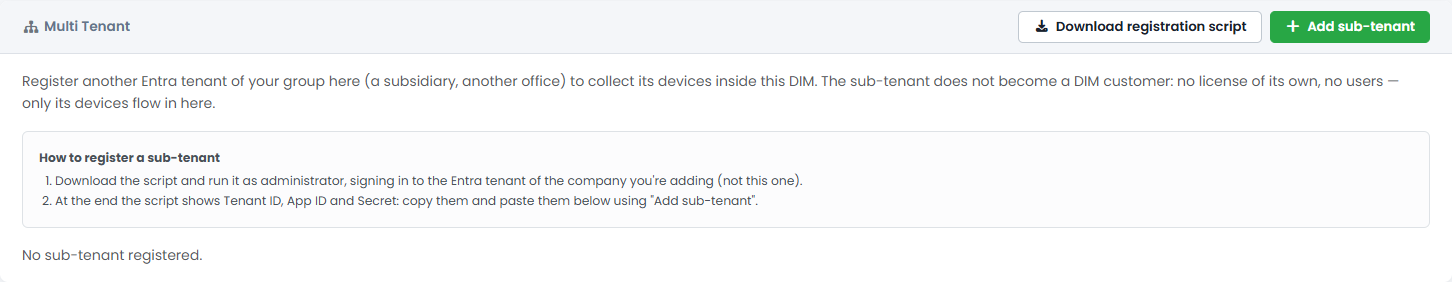
- Click Download registration script.
- Run the script in PowerShell as an administrator, signing in to the Microsoft Entra tenant of the company you are adding, not your own. The script registers in that tenant the application Device Inventory Manager uses to read Microsoft Intune.
- At the end, the script shows the Tenant ID, App ID and Secret. Copy them.
- Back in the portal, click Add sub-tenant and fill in the company name, the three values and the expiry date of the secret. Click Register.
- Click the shield icon on the new row to check that the application has all the permissions it needs.
The devices of the sub-tenant appear after the next synchronization.
Managing sub-tenants
The card lists every sub-tenant with its status, the expiry of its secret and the last synchronization. From each row you can:
| Action | Effect |
|---|---|
| Check Graph permissions (shield) | Checks the permissions of the application in that tenant. |
| Edit sub-tenant | Changes the name or replaces the secret with a new one. |
| Deactivate / Reactivate | Stops or resumes the synchronization, keeping the data. |
| Delete | Permanently deletes the sub-tenant and all its devices, with their history, attachments, Inventory assets and visibility rules. You confirm by typing the company name. |
The secret of each sub-tenant expires. Administrators receive an email reminder in the 30 days before expiry: create a new secret in that tenant and paste it in Edit sub-tenant before it expires, otherwise the devices of that company stop updating.
Working with several companies
- In the device list, the Company filter shows the devices of one company.
- In Device Visibility (RBAC), the Company rule limits a group to the devices of some companies, for example the local IT team of a subsidiary.
- The agent is the same for all companies: one
config.datfrom your tenant works on the devices of every sub-tenant (see Agents).