
Audit Log
The audit log records what people do in the portal on your organization's data: who signed in, which pages and devices they opened, what they imported, exported, changed or deleted. Use it to answer questions such as who changed the warranty of this laptop? or who exported the device list last week?
Open My Tenant › Edit › Audit log. The tab is available to tenant administrators.
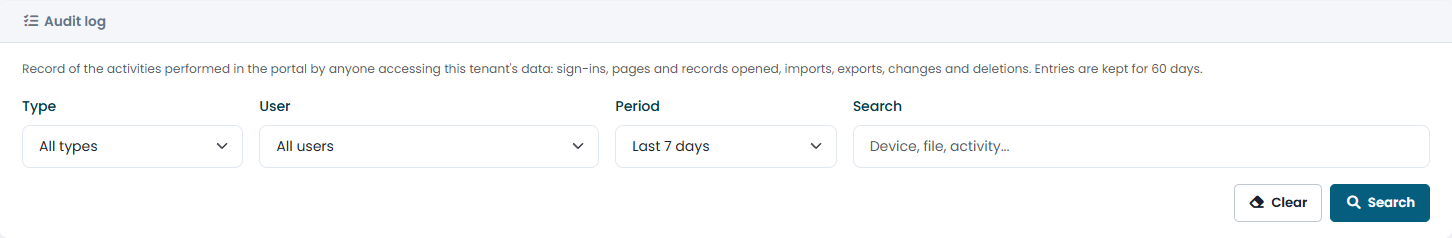
Searching
| Filter | Options |
|---|---|
| Type | Sign-ins, Navigation, Devices, Extra devices, Inventory, Import/Export, Assignments, Administration, Other |
| User | Anyone who has accessed your data in the last 60 days |
| Period | Last 24 hours, 7 days, 30 days or 60 days |
| Search | Free text, searched in the activity and its details: a device name, a file name, an action |
Click Search to apply the filters and Clear to reset them.
Each entry shows the date and time (in your time zone), the user, the type, the activity, its details and the IP address it came from.
What is recorded
- Sign-ins of users and administrators.
- Pages and records opened, for example a device page.
- Files downloaded, imports and exports.
- Changes and deletions of devices, extra devices, Inventory assets and assignments.
- Administrative changes: users and permissions, settings, notifications, MSP access, sub-tenants.
The list includes everyone who has accessed your data, including Inside Technologies support staff and any managed service provider you have authorized. Automatic activities of the platform, such as the nightly synchronization with Microsoft Intune, are not shown.
Exporting
Click Export CSV to download the entries that match the current filters, up to 50,000 rows. The export itself is recorded in the log. To export, a user needs the Export Audit Log permission (see Users & Permissions).
Retention
Entries are kept for 60 days and then deleted. Export them regularly if you need to keep them longer.