
Compliance Assessments
The technical assessments tell you how your systems are configured. Regulations ask a broader question: does your organization have the processes, roles and controls the law requires? Compliance Assessments help you answer it with guided questionnaires, one per regulation, that turn the legal text into concrete questions and give you a readiness report.
The questionnaires provide an indicative assessment. They do not replace legal advice or a certified audit: use them to understand where you stand, to plan the work, and to prepare the conversation with your advisors and auditors.
Available Regulations
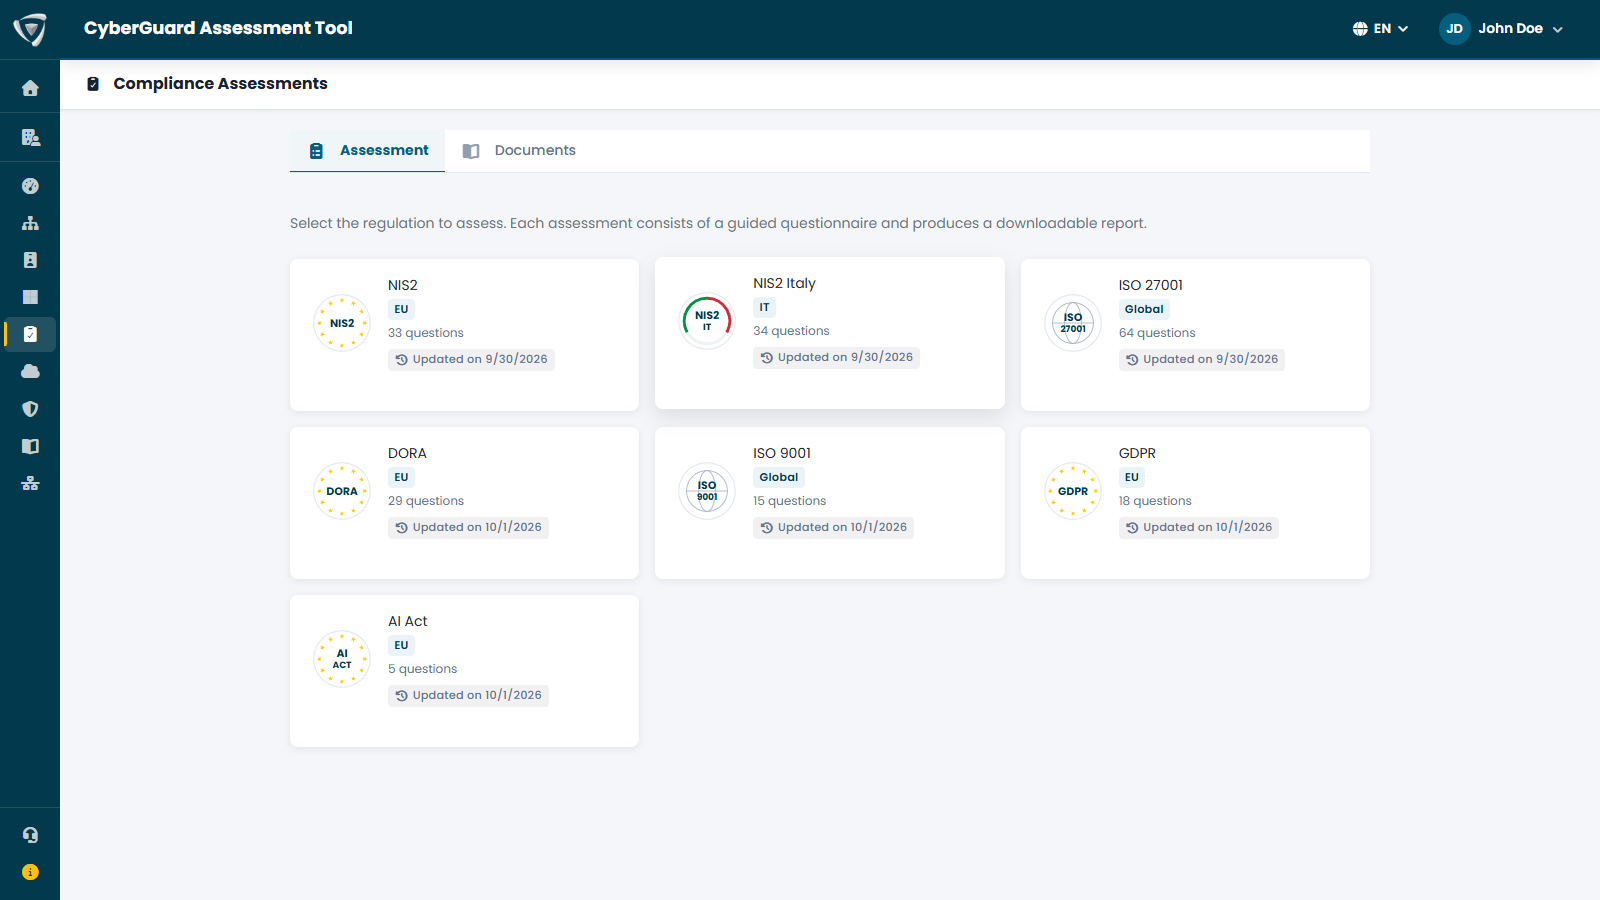
From Assessment → Compliance Assessments, choose the regulation to assess. Each card shows its scope (European, national or global), how many questions it contains and when it was last updated. Today the questionnaires cover:
| Regulation | Scope |
|---|---|
| NIS2 | The EU directive on the security of network and information systems. |
| NIS2 Italy | The Italian transposition of NIS2, with the obligations set by the national authority (ACN). |
| DORA | The EU regulation on the digital operational resilience of the financial sector. |
| GDPR | The EU regulation on the protection of personal data. |
| AI Act | The EU regulation on artificial intelligence. |
| ISO 27001 | The international standard for information security management. |
| ISO 9001 | The international standard for quality management. |
Each regulation has a short description of what it requires and to whom it applies, Start assessment to fill in a new questionnaire and Assessment History to open the ones already completed.
Filling In a Questionnaire
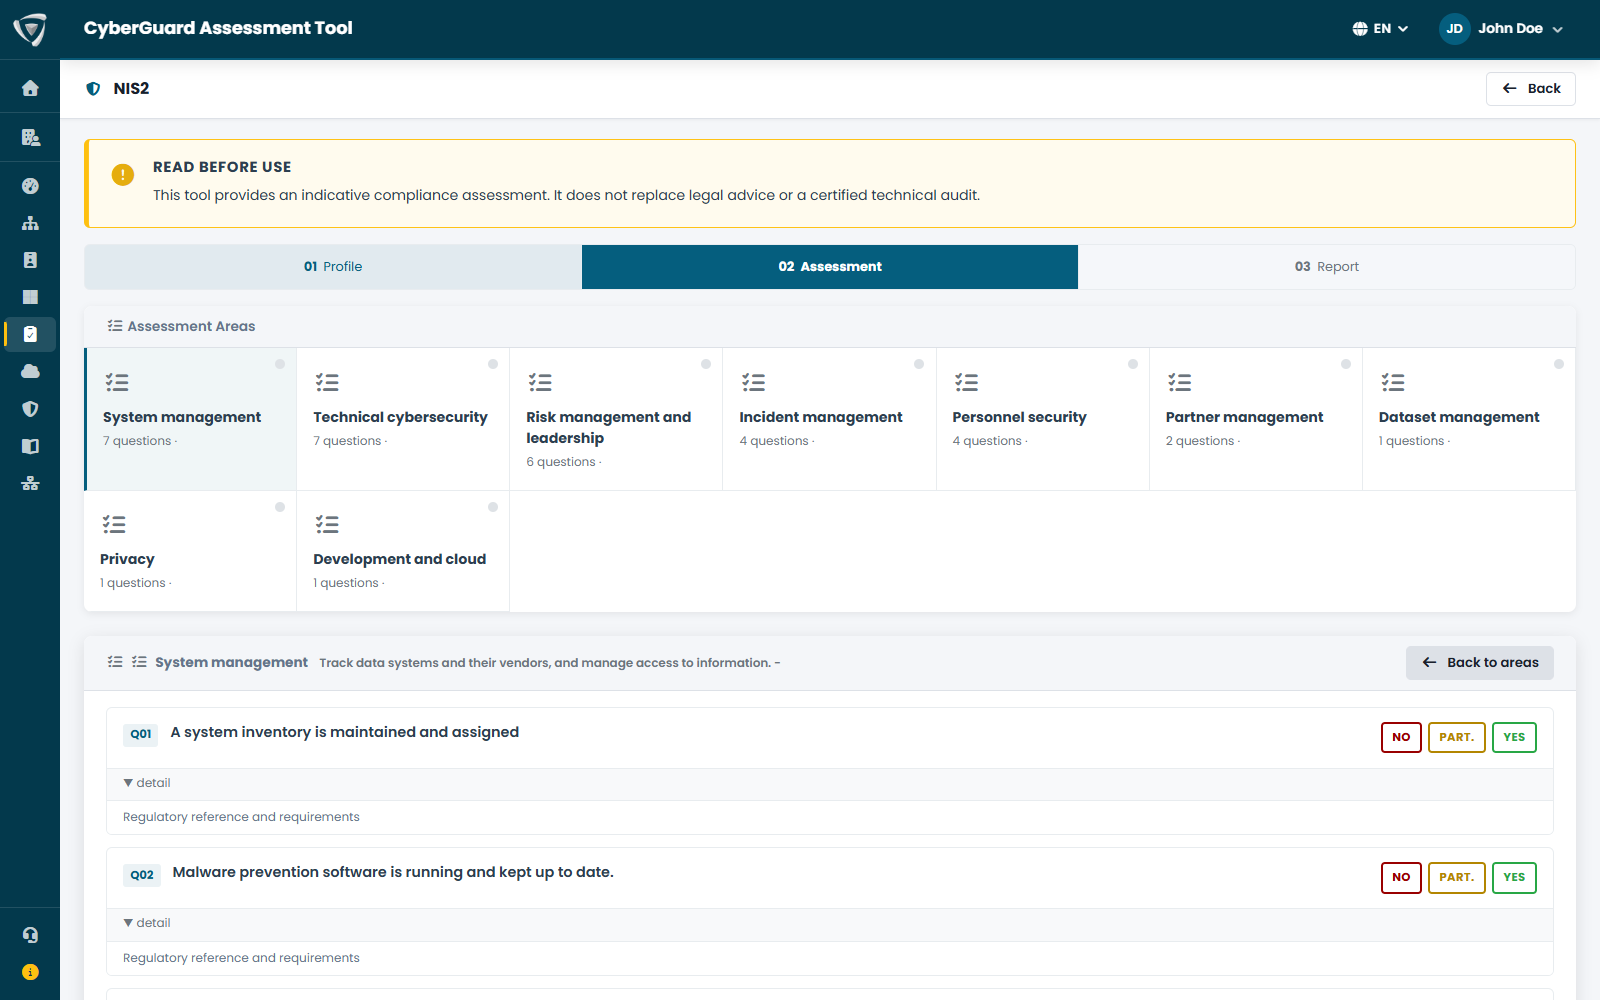
A questionnaire has three steps:
- Profile — a few questions about your organization, used to understand whether and how the regulation applies to you.
- Assessment — the questions, grouped by area (for example system management, incident management, personnel security, partner management). Answer each one with No, Partial or Yes.
- Report — your readiness level, overall and area by area, with the gaps to close. The report is saved when all questions have an answer, and you can download it.
Support With the Legal References
You don't need to know the regulation by heart to answer. Under each question:
- detail explains what a No, a Partial and a Yes mean in practice, so that the answer is consistent across people and over time;
- Regulatory reference and requirements shows the article of the regulation the question comes from and the requirements it sets.
This way every gap in the report is tied to the legal text it comes from, which makes it easier to explain why a control is needed and to plan the remediation.
Documentation
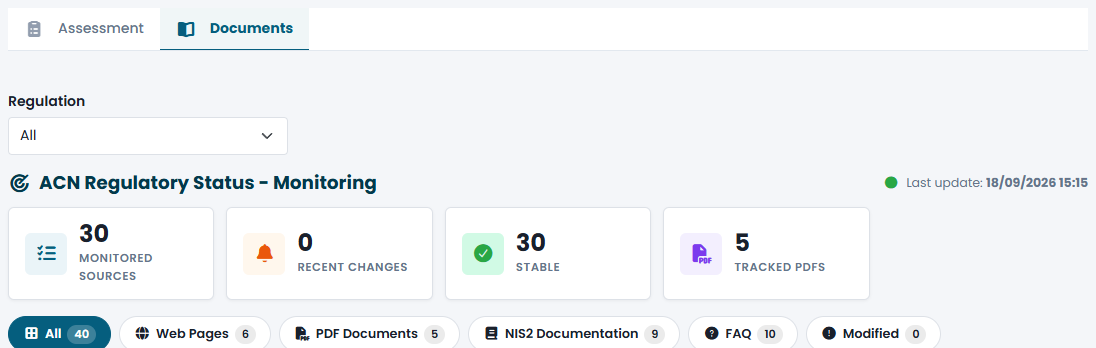
The Documents tab collects the official sources behind the questionnaires: legal texts, guidelines of the authorities, FAQs and reference documents, filterable by regulation and by type (web pages, PDF documents, FAQ).
For NIS2 in Italy, CyberGuard also monitors the regulatory status published by the national authority: the counters show how many sources are monitored, how many changed recently and how many PDF documents are tracked, so you know when something you rely on has been updated. Use Modified to see only the sources that changed.
Using the Results
- Repeat the questionnaire periodically and compare the reports in Assessment History to show progress.
- Combine it with the technical assessments: many requirements — access control, MFA, logging, backups, vulnerability management — are verified in practice by the Active Directory, Microsoft Entra and Microsoft 365 assessments.
- Record the actions you plan in the Workspace, in the Compliance area.